PowerShell Threat Hunting in Defender XDR
Review PowerShell behaviour in context and practise a hypothesis-led hunt using harmless synthetic records.
Explore courseI’m Caleb, known online as Smitti. I share practical lessons, guided labs and ideas to help you understand cybersecurity and put your knowledge to work.
# Start with observation.
Get-Process |
  Sort-Object ProcessName |
Select-Object -First 10Build understanding one lesson at a time, with guided practice and knowledge checks.
Review PowerShell behaviour in context and practise a hypothesis-led hunt using harmless synthetic records.
Explore courseFind the right evidence store, document actual retention and reason about events that arrive after a detection window.
Explore courseBuild an evidence-led email triage workflow and a reviewed containment plan without making live tenant changes.
Explore courseVideo-led explanations from CyberSecurityWithSmitti. Press play when you’re ready.
Read the code, understand its effects and test responsibly before applying it.
Compare selected scalar fields across two trusted JSON array snapshots.
Read the exampleReport available protection status and preferences; exclusions are explicit opt-in.
Read the exampleCollect active-store inbound allow rules with related ports, addresses and programs.
Read the exampleExplore my tools and engineering projects: the problems, the implementation and the evidence behind each build.
9 projects
 Enhanced screenshot
KQL tooling
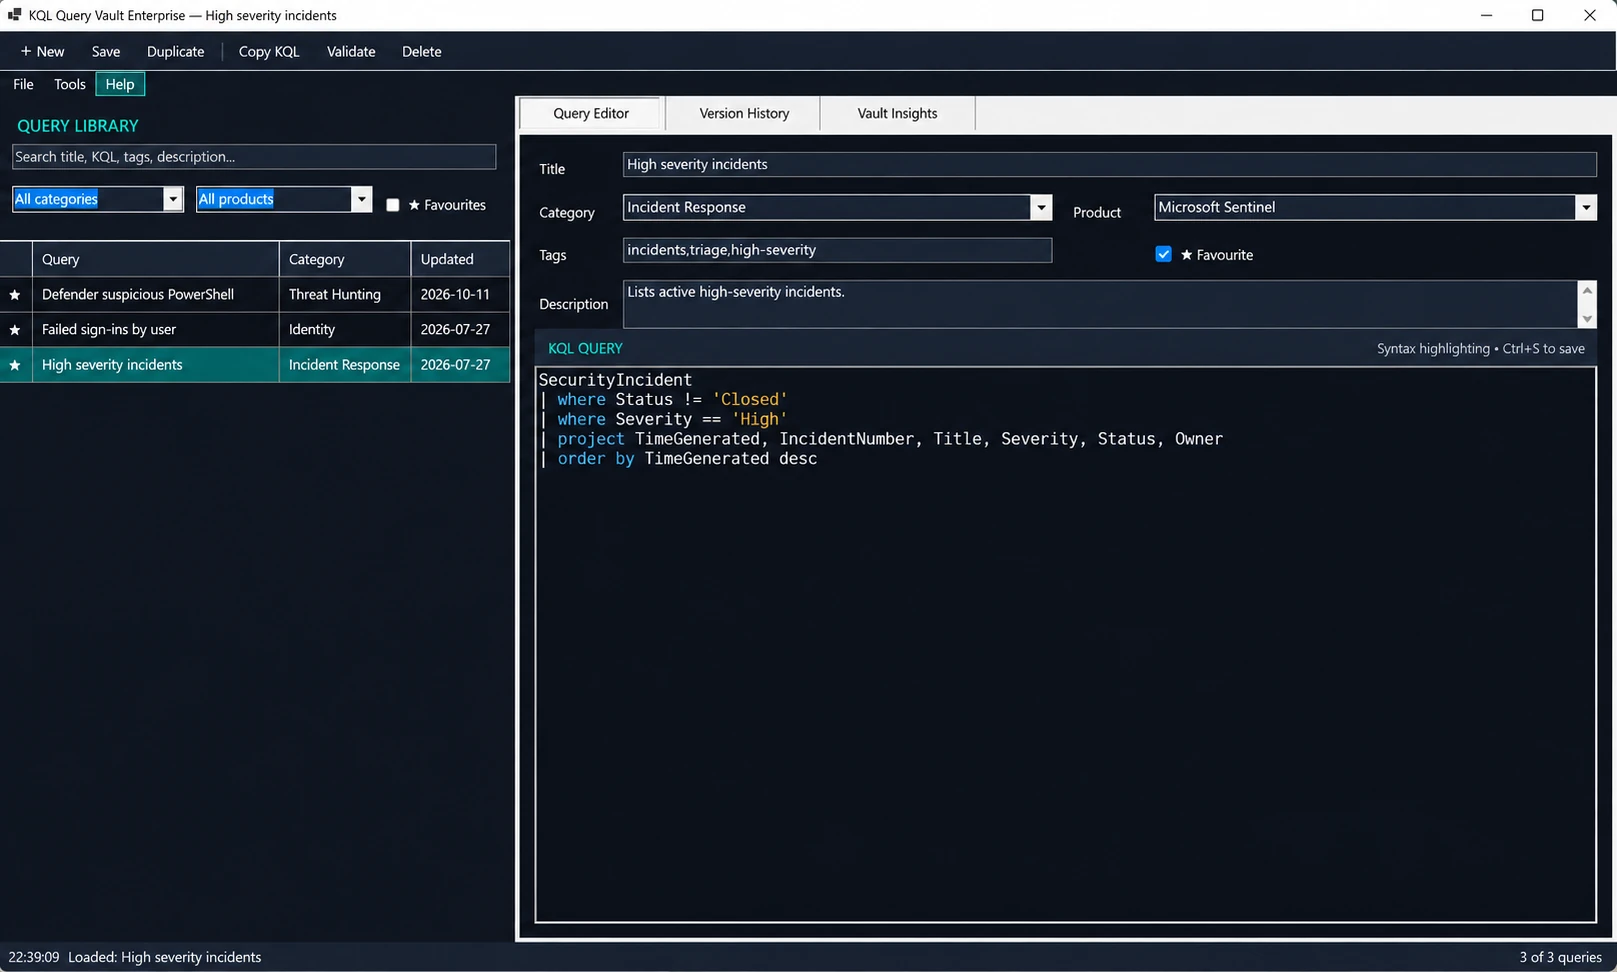
A local query library that makes KQL easier to organise, edit, reuse and recover.
Read case study: KQL Query Vault Enterprise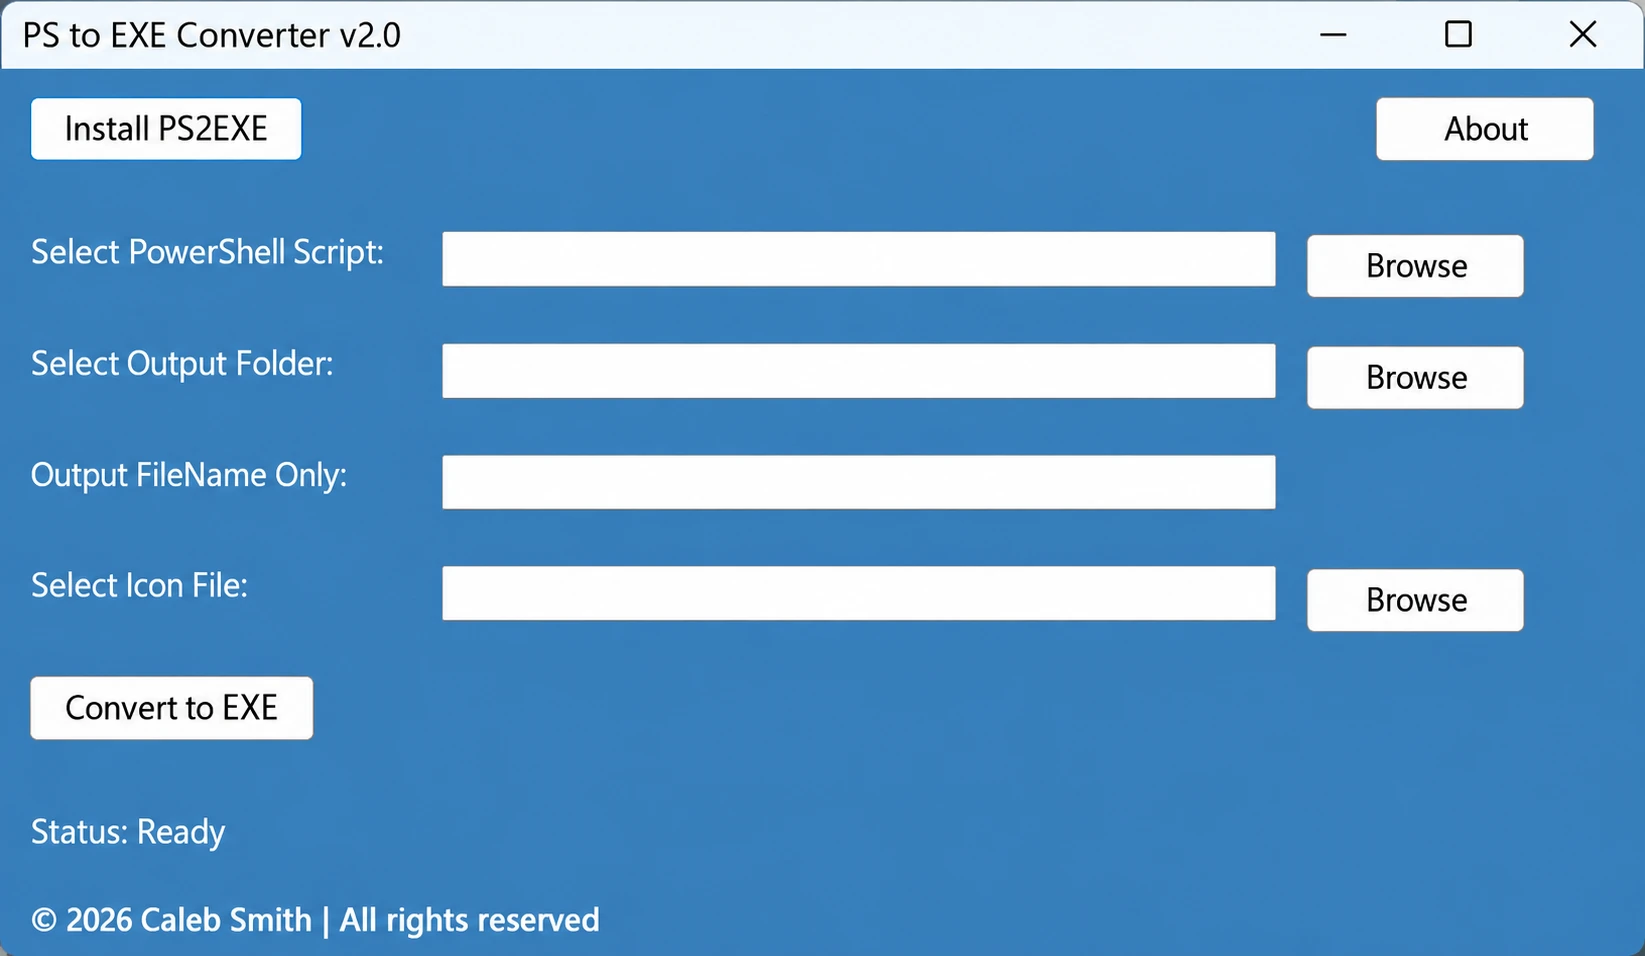 Enhanced screenshot
PowerShell tools
A straightforward Windows interface for packaging a PowerShell script with PS2EXE.
Read case study: PowerShell to EXE Converter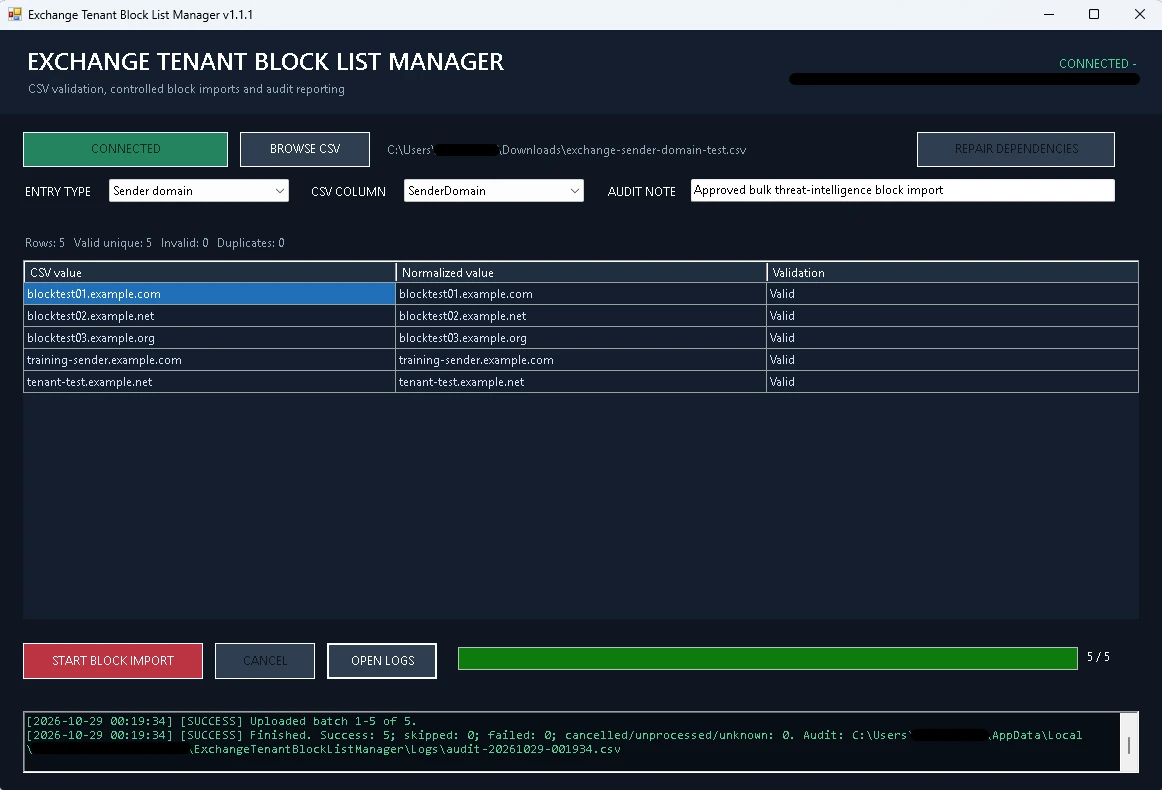 Application capture
PowerShell tools
A Windows tool for validating CSV block entries, controlling Exchange Online imports and retaining an audit of each outcome.
Read case study: Exchange Tenant Block List Manager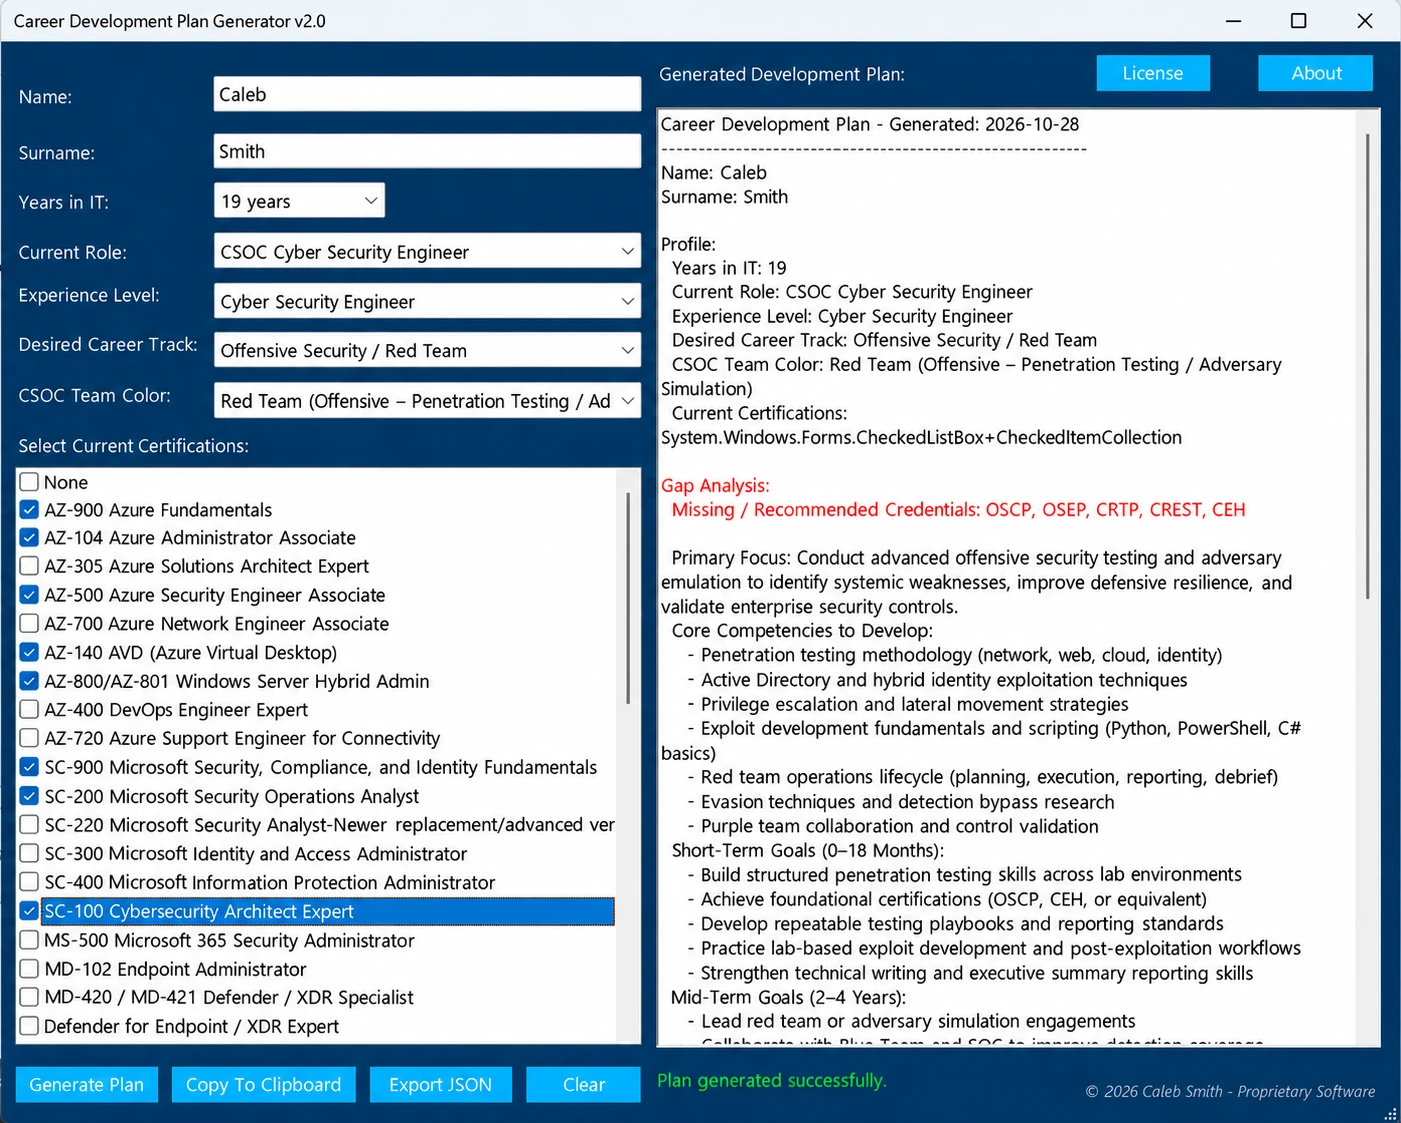 Enhanced screenshot
PowerShell tools
Turn experience, career direction and selected qualifications into a structured development plan.
Read case study: Career Development Plan Generator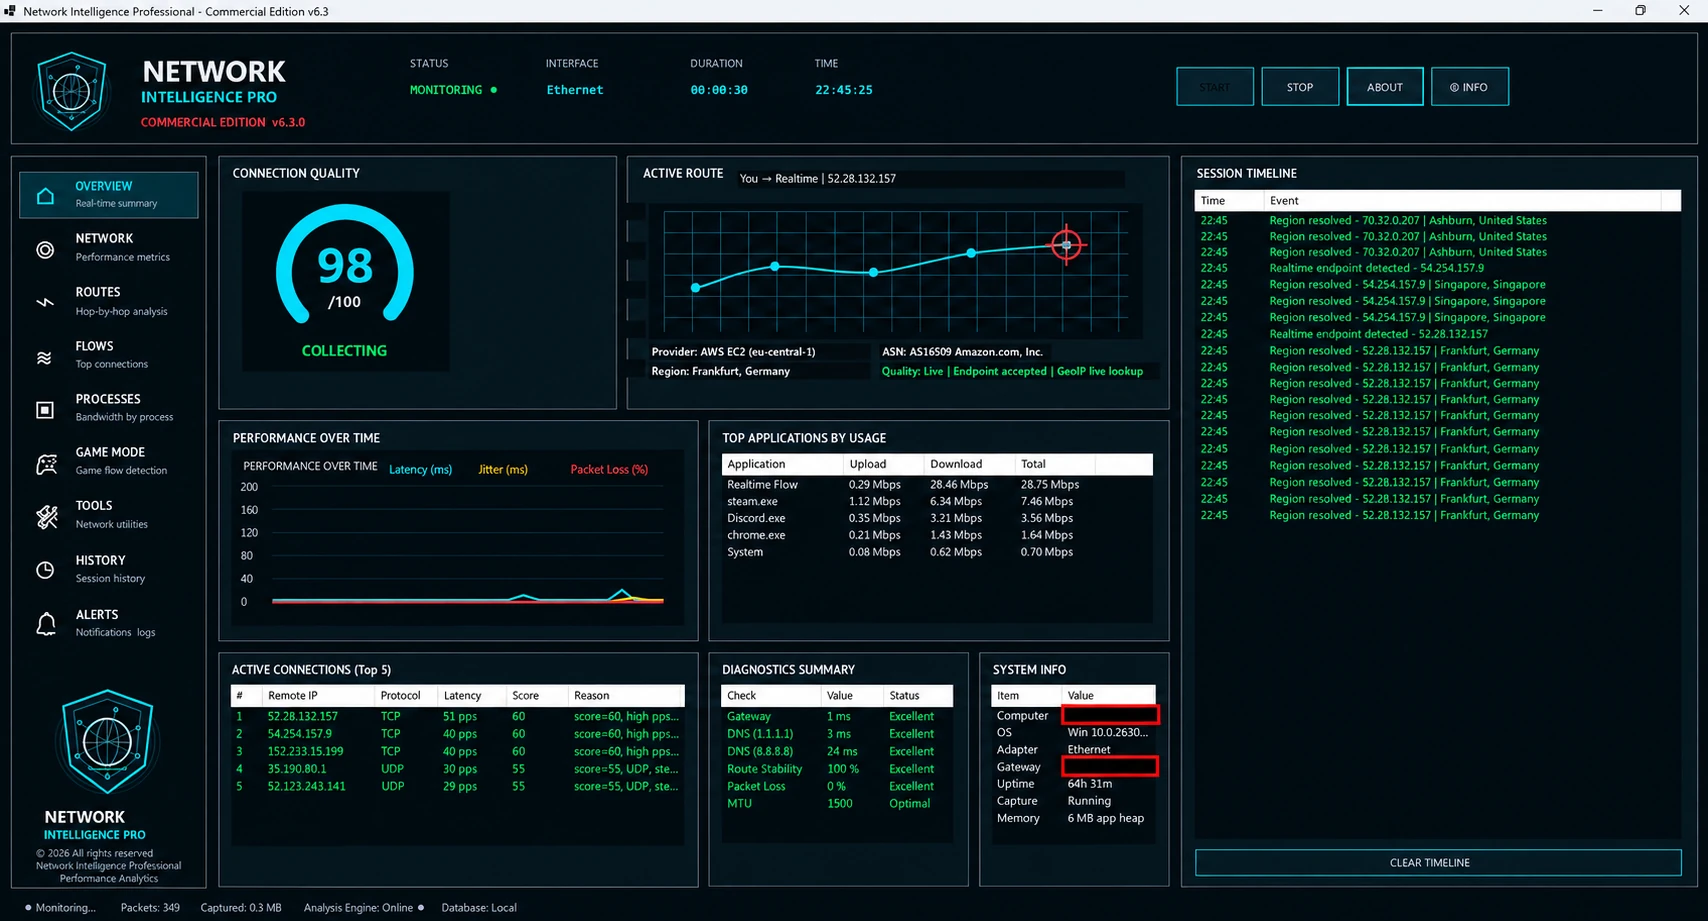 Enhanced screenshot
Security engineering
A Windows dashboard for connection visibility, route diagnostics and network performance.
Read case study: Network Intelligence Professional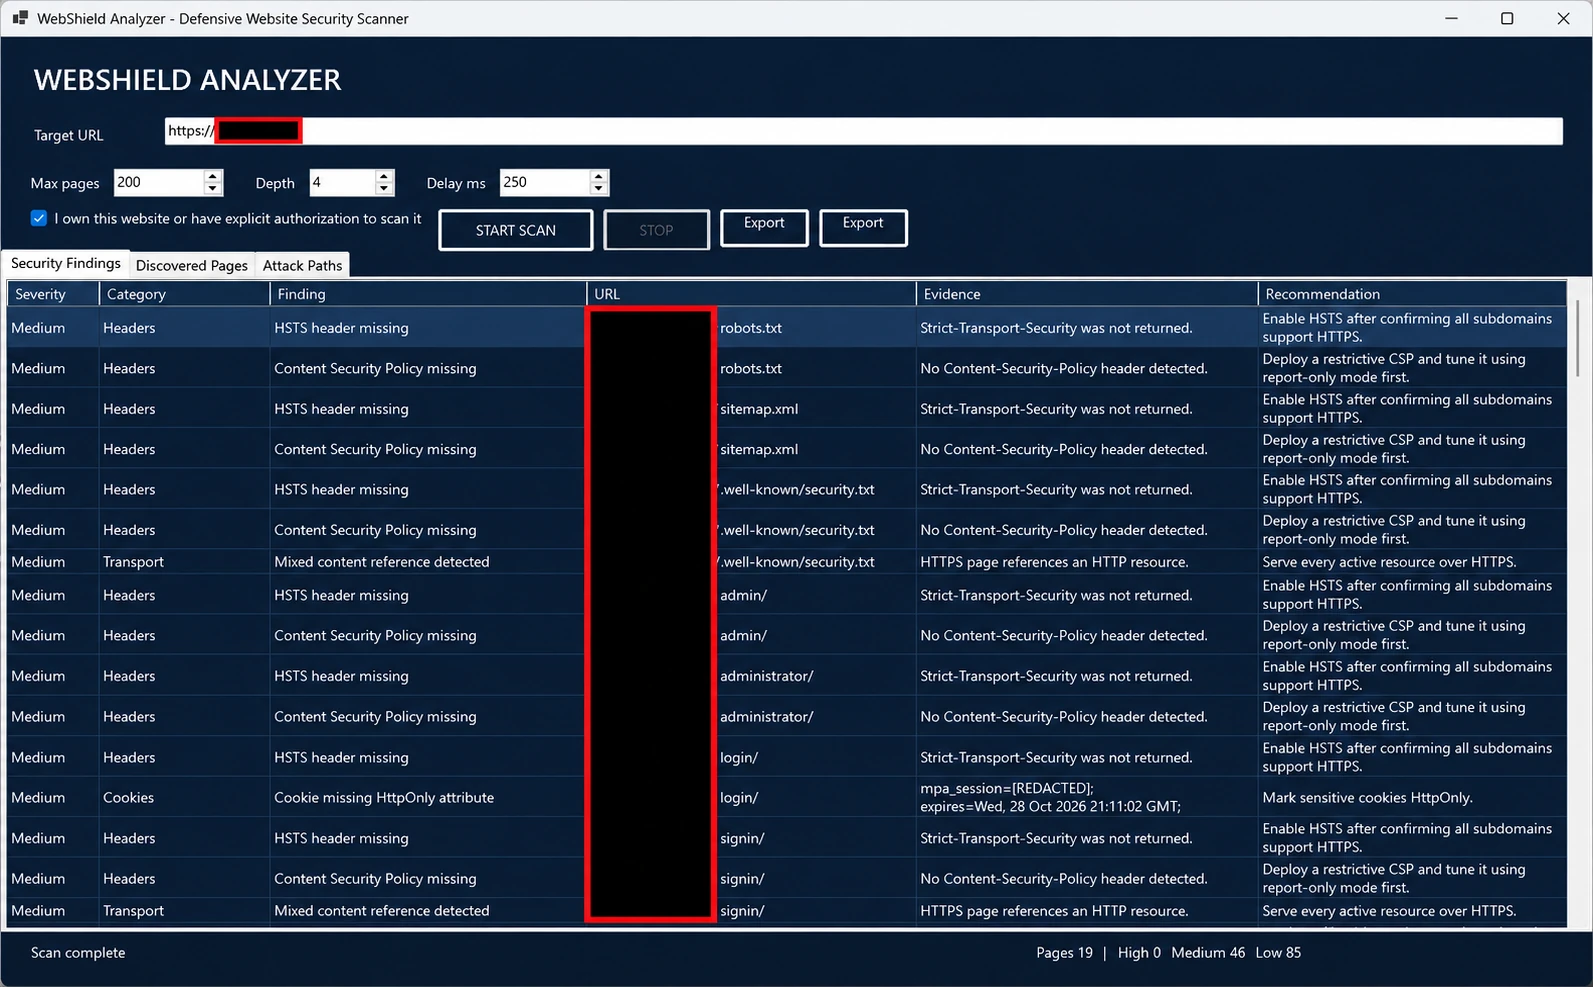 Enhanced screenshot
Security engineering
A Windows interface for defensive website checks, with scan controls, findings and export actions.
Read case study: WebShield Analyzer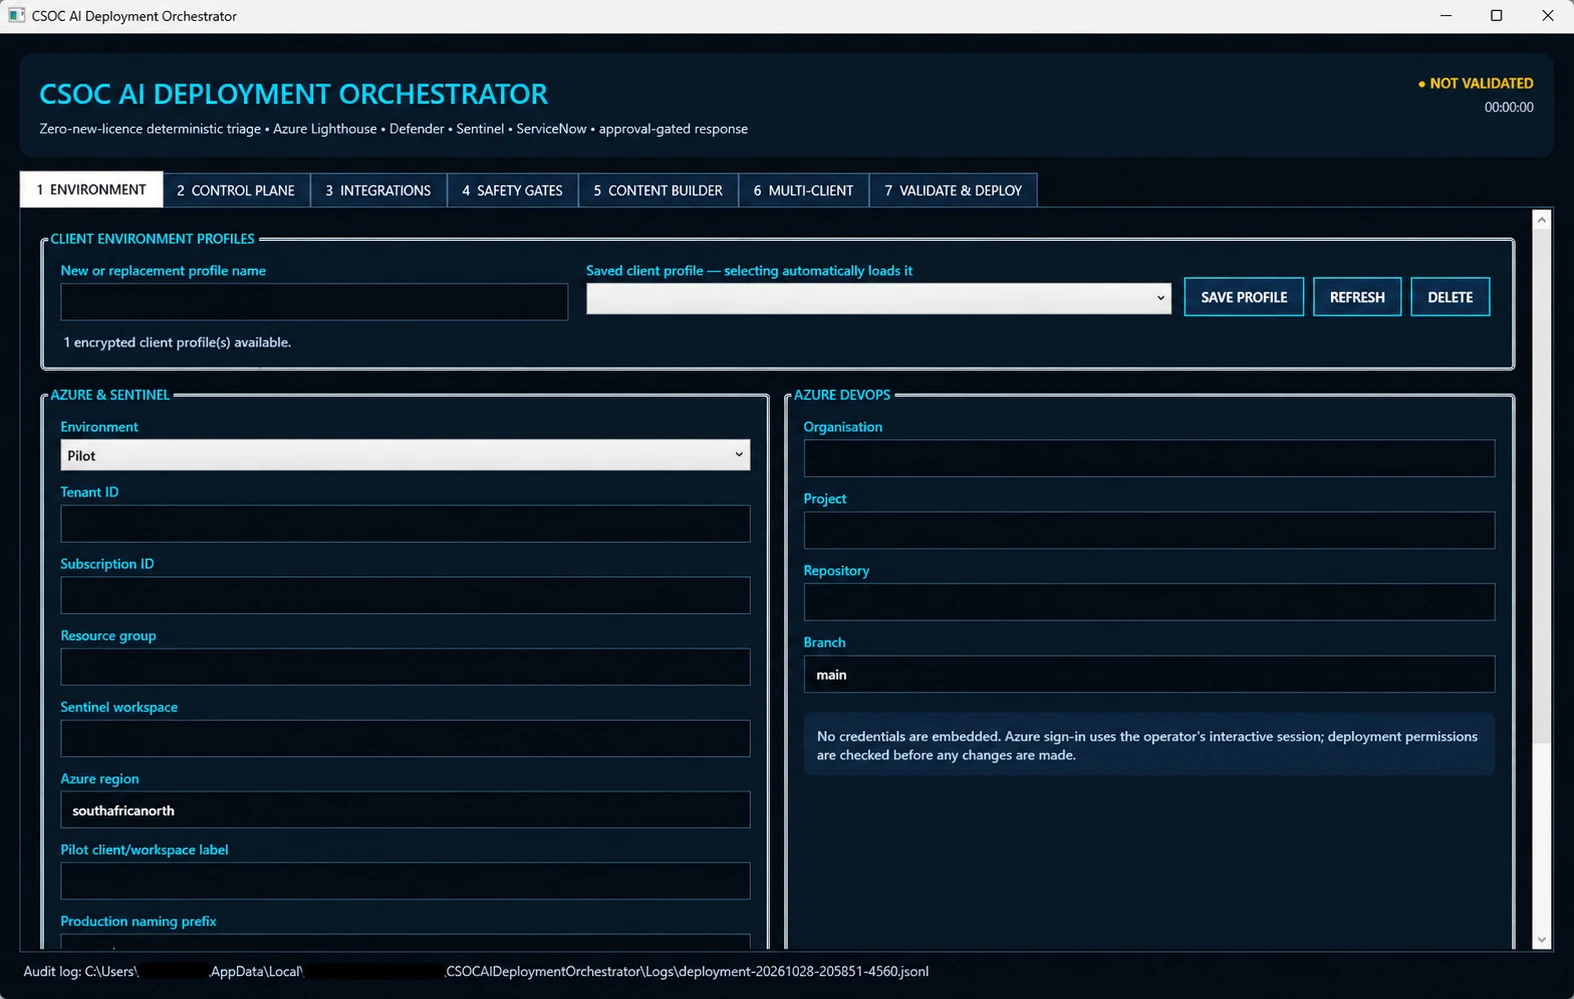 Enhanced screenshot
Security engineering
A controlled path from SOC deployment planning to verified change, with the operator in control.
Read case study: CSOC Deployment Orchestrator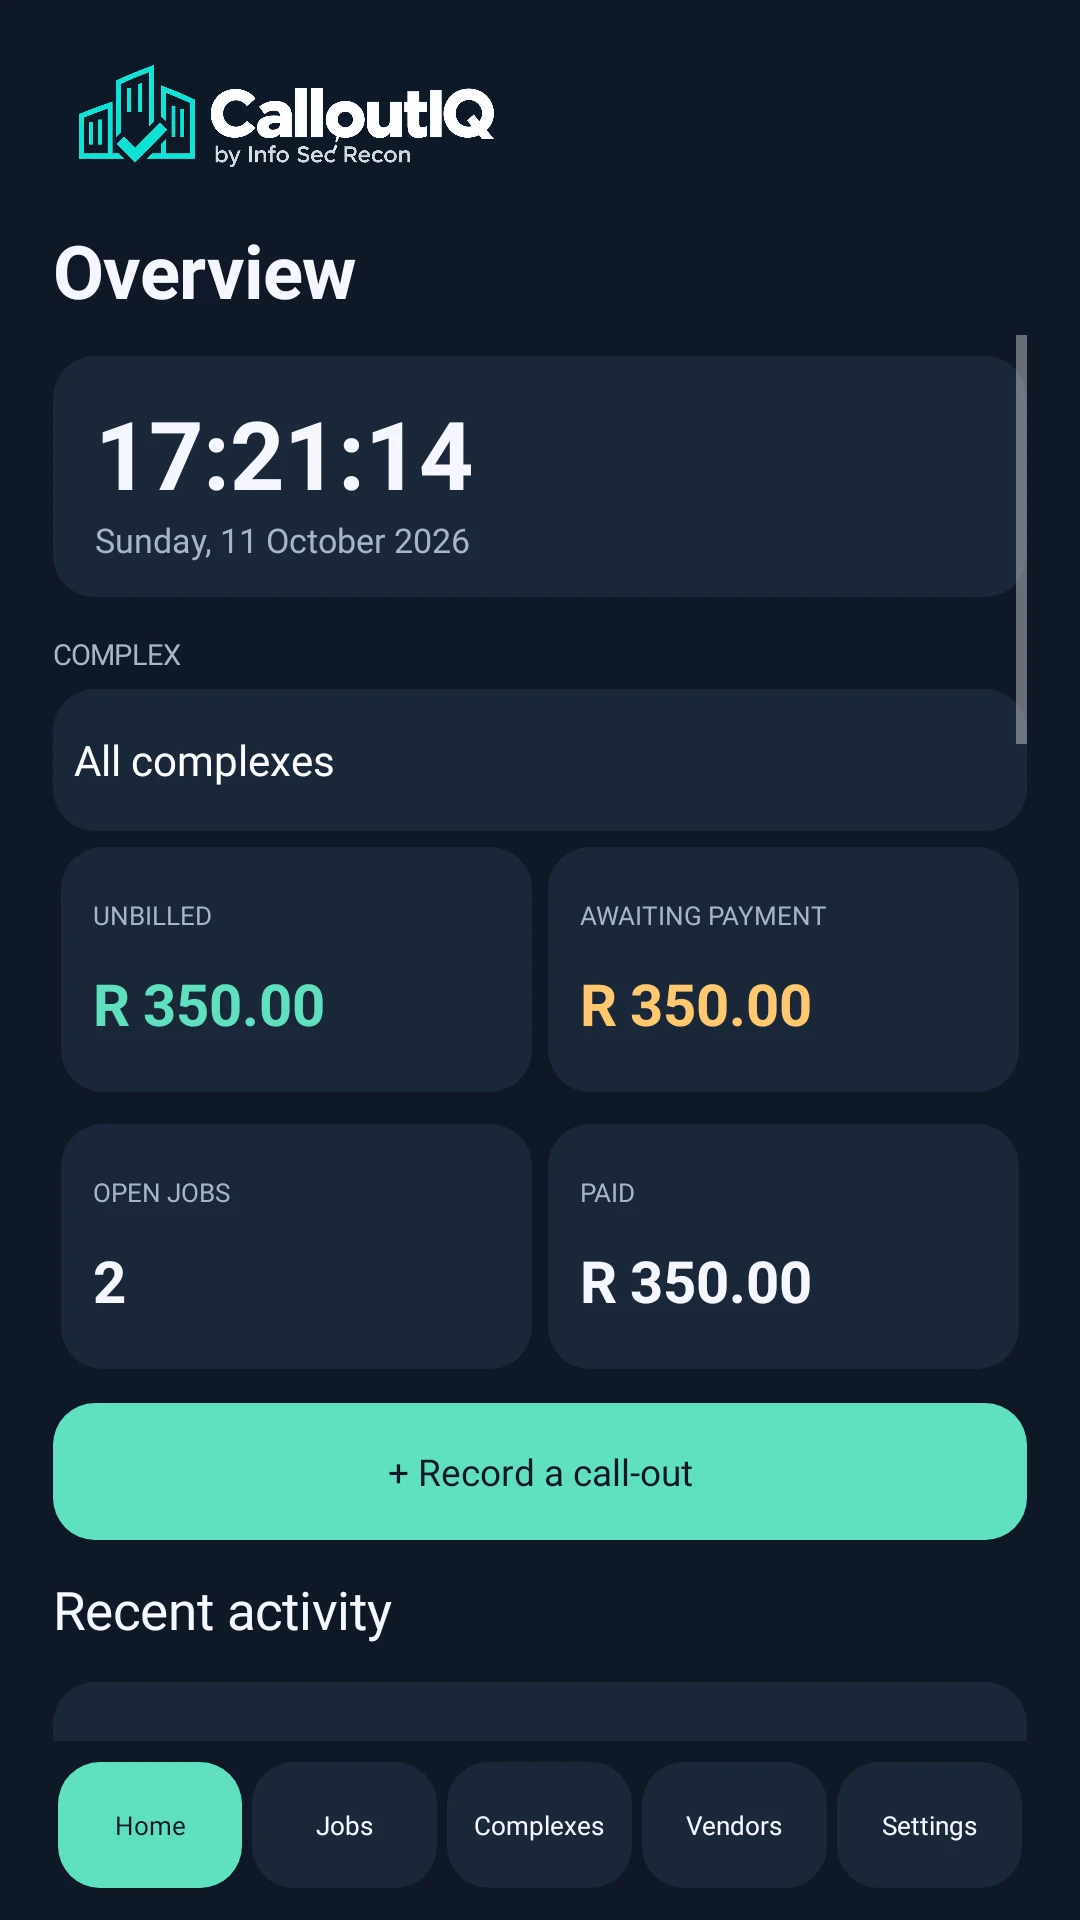
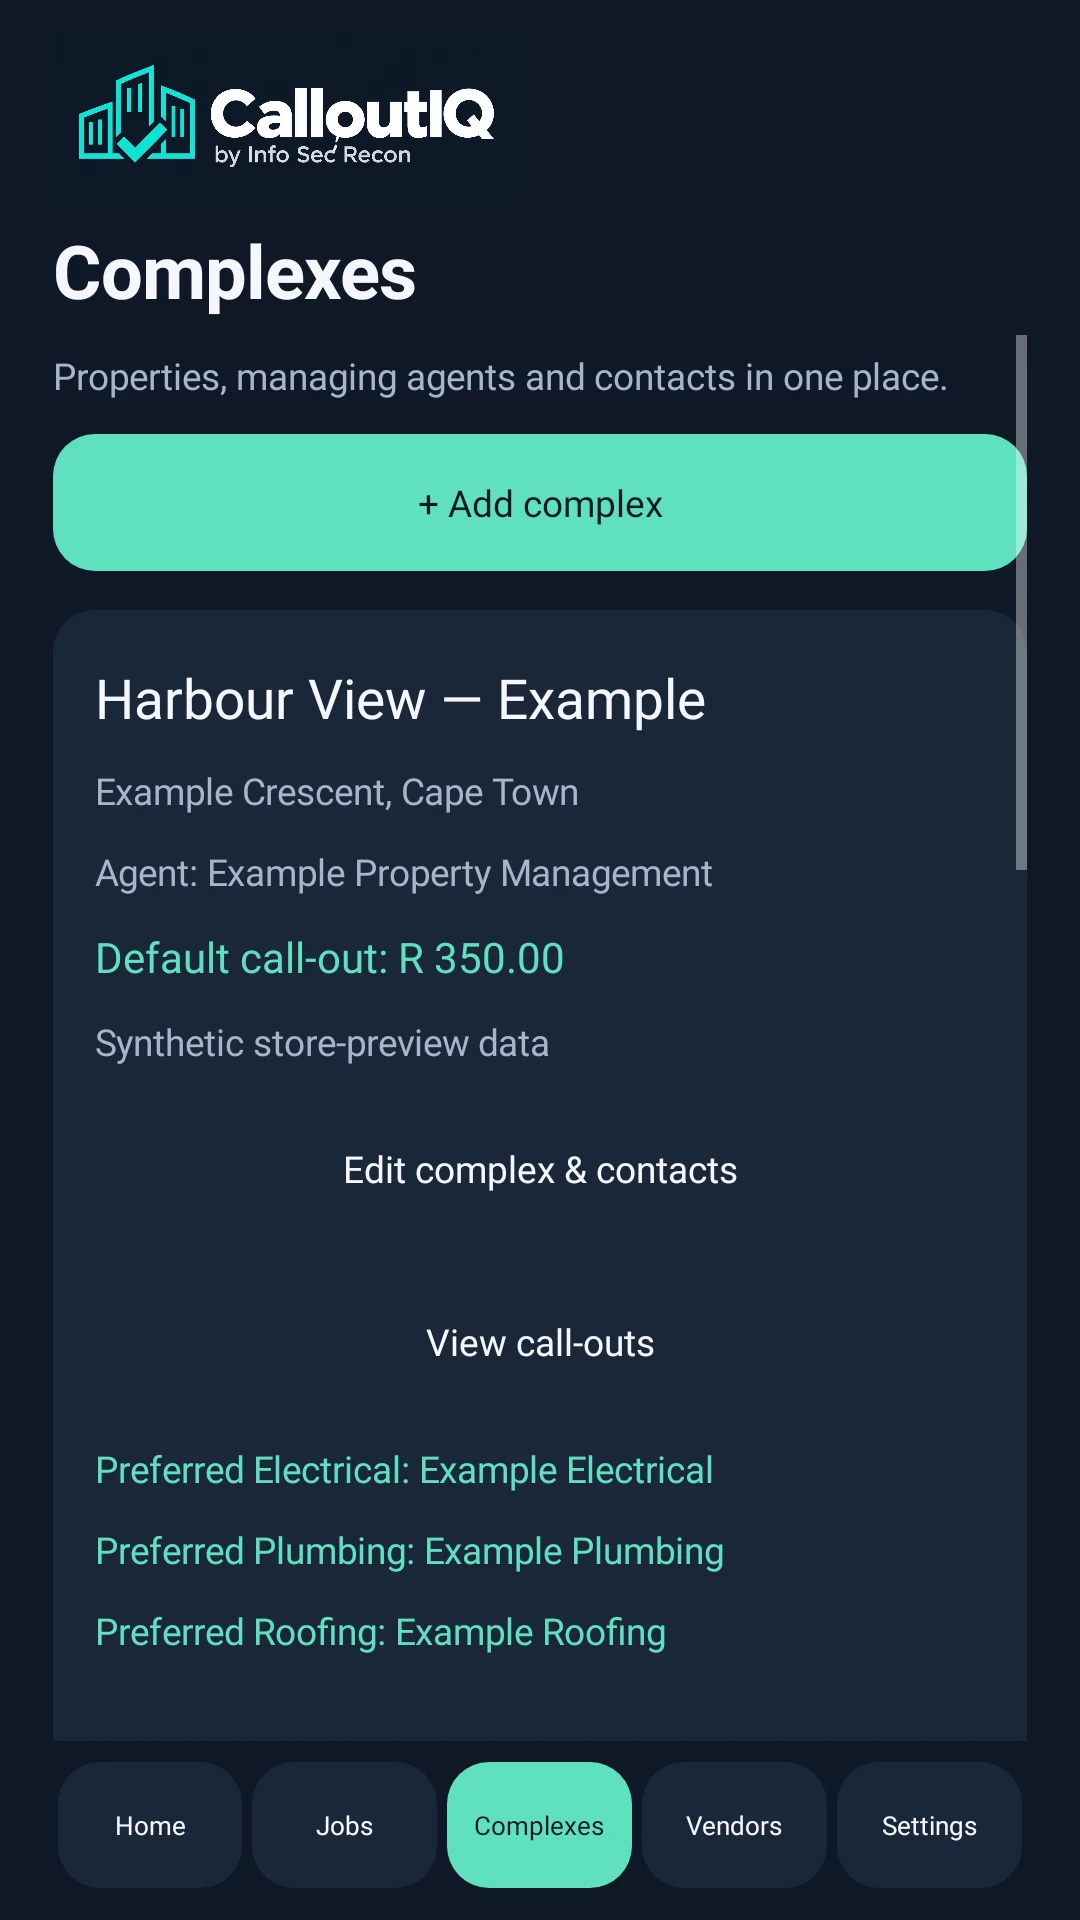
Mobile applications
From a repeated maintenance call to a clear record of the work, the fee and the payment status.
Read case study: CallOutIQ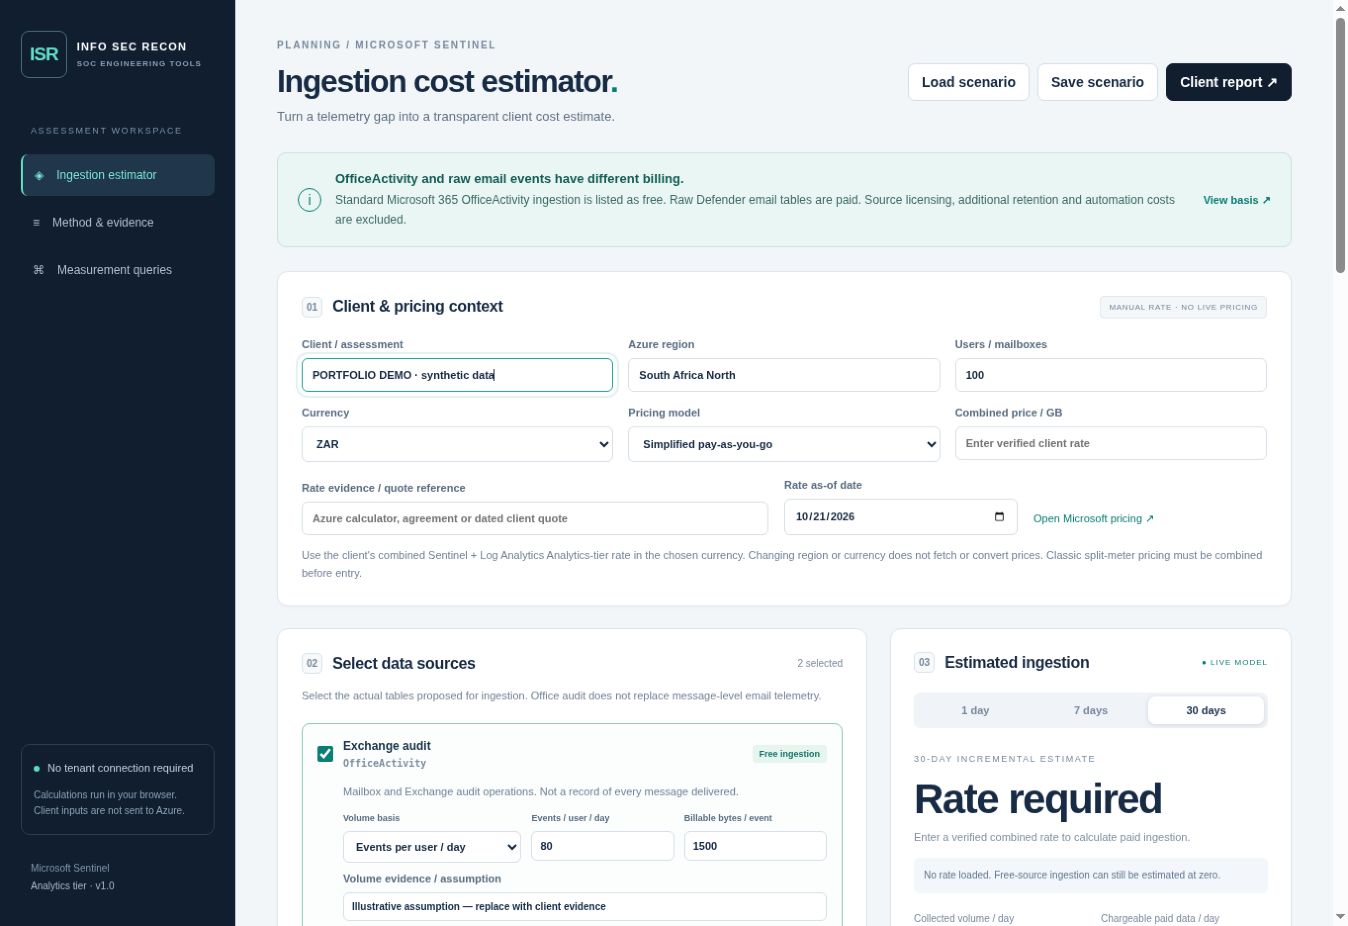 Original capture · synthetic inputs
SOC tooling
Make the assumptions behind a telemetry estimate visible, traceable and easy to explain.
Read case study: Sentinel Ingestion EstimatorTry another search or reset the filters.
Open a project to explore its purpose, implementation and validation scope.
A local query library that makes KQL easier to organise, edit, reuse and recover.
Useful investigation queries become difficult to maintain when they are scattered across files and notes, with little history or consistent categorisation.
A Windows query-management application with a searchable library, category and product filters, an editor, version history and JSON vault import/export.
The supplied executable contains the application assembly and a bundled Windows runtime. Embedded interface strings and application methods were inspected to verify the feature descriptions. Runtime behaviour was not re-tested on Windows for this portfolio. A supplied application screenshot is also included, with the enhanced preview identified separately from the original capture.
The offline validator checks basic structural issues such as unbalanced brackets and duplicated pipes. It does not run KQL, verify tenant table/column names or establish detection effectiveness.
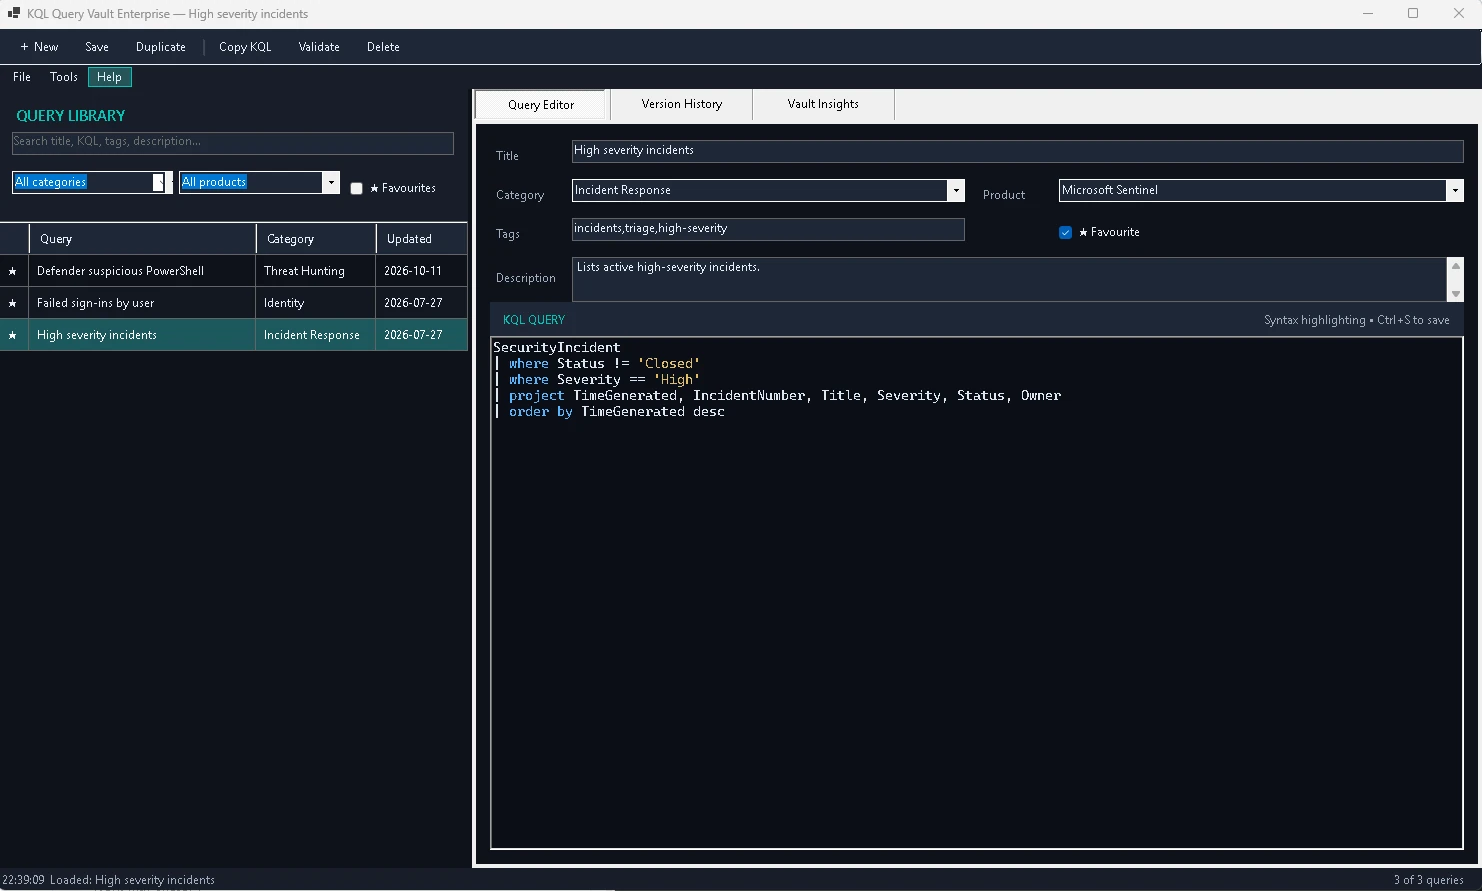
Evidence reviewed: the supplied KQLQueryVaultEnterprise executable and its embedded application assembly. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsA straightforward Windows interface for packaging a PowerShell script with PS2EXE.
Packaging a script involves selecting the source, choosing an output location and applying the right build options repeatedly.
A PowerShell Windows Forms front end for the PS2EXE module, with source and output selection, executable naming, an icon picker and build-status feedback.
The supplied v2 script was inspected. Its event handlers invoke PS2EXE and provide file/folder pickers and status messages. A conversion was not executed during this portfolio review. A supplied application screenshot is also included, with the enhanced preview identified separately from the original capture.
This is a GUI wrapper around PS2EXE, not a compiler engine written from scratch. Packaging does not by itself provide code signing, source-code secrecy or compatibility with every execution-control policy.
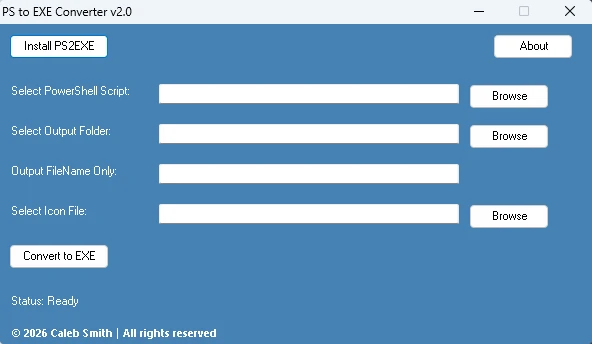
Evidence reviewed: the supplied PS to EXE Converter v2 PowerShell script. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsA Windows tool for validating CSV block entries, controlling Exchange Online imports and retaining an audit of each outcome.
Bulk mail-security block imports combine module dependencies, inconsistent CSV values, existing entries and changes that can affect mail flow. Operators need to review the inputs and see exactly what was attempted.
A PowerShell Windows Forms interface with dependency preflight and recovery, normalized CSV previews, explicit account confirmation, bounded batches, cancellation and per-value audit records.
The supplied v1.1.1 Windows capture shows a connected Exchange session, five valid unique sender domains and a completed import: 5 successful, 0 failed, with an audit CSV path reported. Corrected source v1.1.1 also passed 57 local assertions using dependency fixtures and mocked import operations. The screenshot documents the application-reported result; tenant entries were not independently inspected during this portfolio review.
The demonstrated Windows test covers a five-entry sender-domain import using example domains. Other entry types, larger imports and tenant-specific permissions, licensing and quotas require separate acceptance checks. The edited script must be re-signed under the operator’s existing signing policy.
Evidence reviewed: supplied PowerShell source, corrected v1.1.1 source and local validation results, plus the user-supplied Windows screenshot of the completed five-domain test.
Back to projectsTurn experience, career direction and selected qualifications into a structured development plan.
A development conversation needs a clear starting profile, an agreed direction and a practical sequence of actions.
A template-driven PowerShell desktop application that takes role, experience, career track and certification inputs and generates a development plan with a high-level 12-month roadmap.
The attached V2.3-named script was inspected. The plan-building function, track templates, gap comparison and JSON export are present. Runtime generation was not re-tested during this review; internal version labels differ from the upload filename. A supplied application screenshot is also included, with the enhanced preview identified separately from the original capture.
The output follows configured templates and rules. It is a planning aid, not an independent assessment of competence or a guarantee of promotion or certification suitability. The supplied output also shows a certification-list formatting issue; it is preserved in both the source capture and enhanced preview.
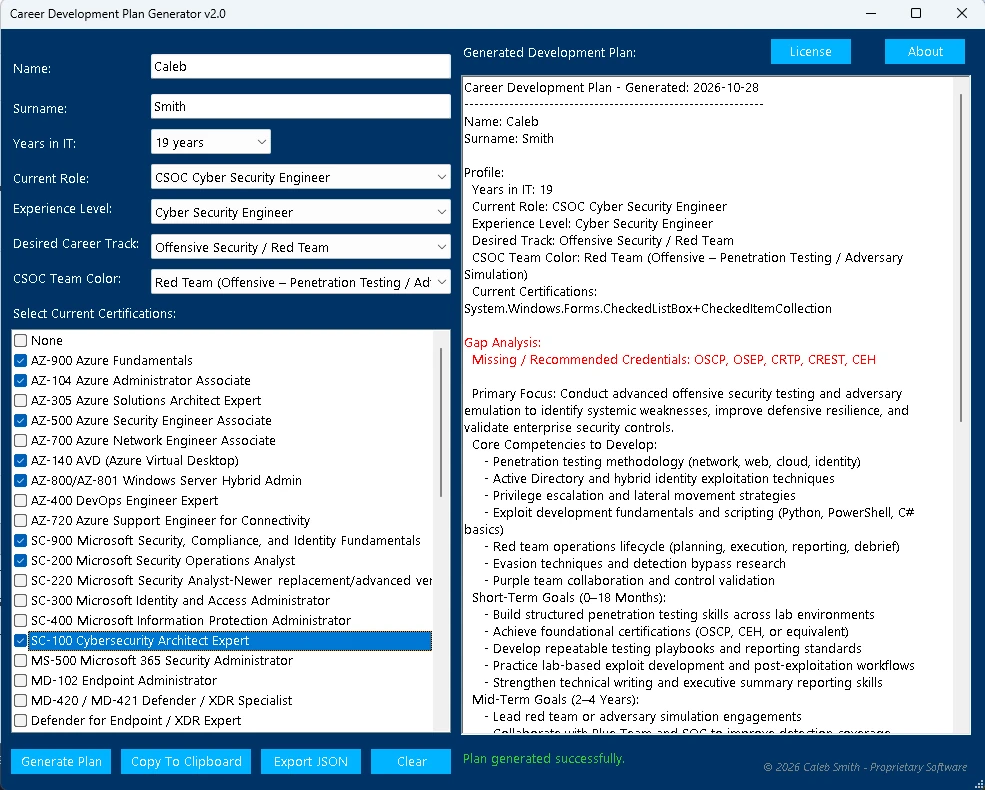
Evidence reviewed: the supplied Career Development Plan Generator PowerShell script. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsA Windows dashboard for connection visibility, route diagnostics and network performance.
The project focuses on making network intelligence and route diagnostics available through a dedicated desktop application.
A versioned Windows application supplied as part of the engineering toolset. The inspected product metadata identifies its network-intelligence and route-diagnostics purpose.
The supplied screenshot shows Commercial Edition v6.3.0 and the overview interface. The earlier uploaded launcher metadata identified v6.1.0 and still requires its companion DLL. These are separate supplied artifacts; their runtime behaviour and metric calculations were not re-tested.
The screenshot supports the visible interface description. It does not independently establish the accuracy of scores, route attribution, diagnostics or bandwidth measurements. Host and gateway values remain redacted.
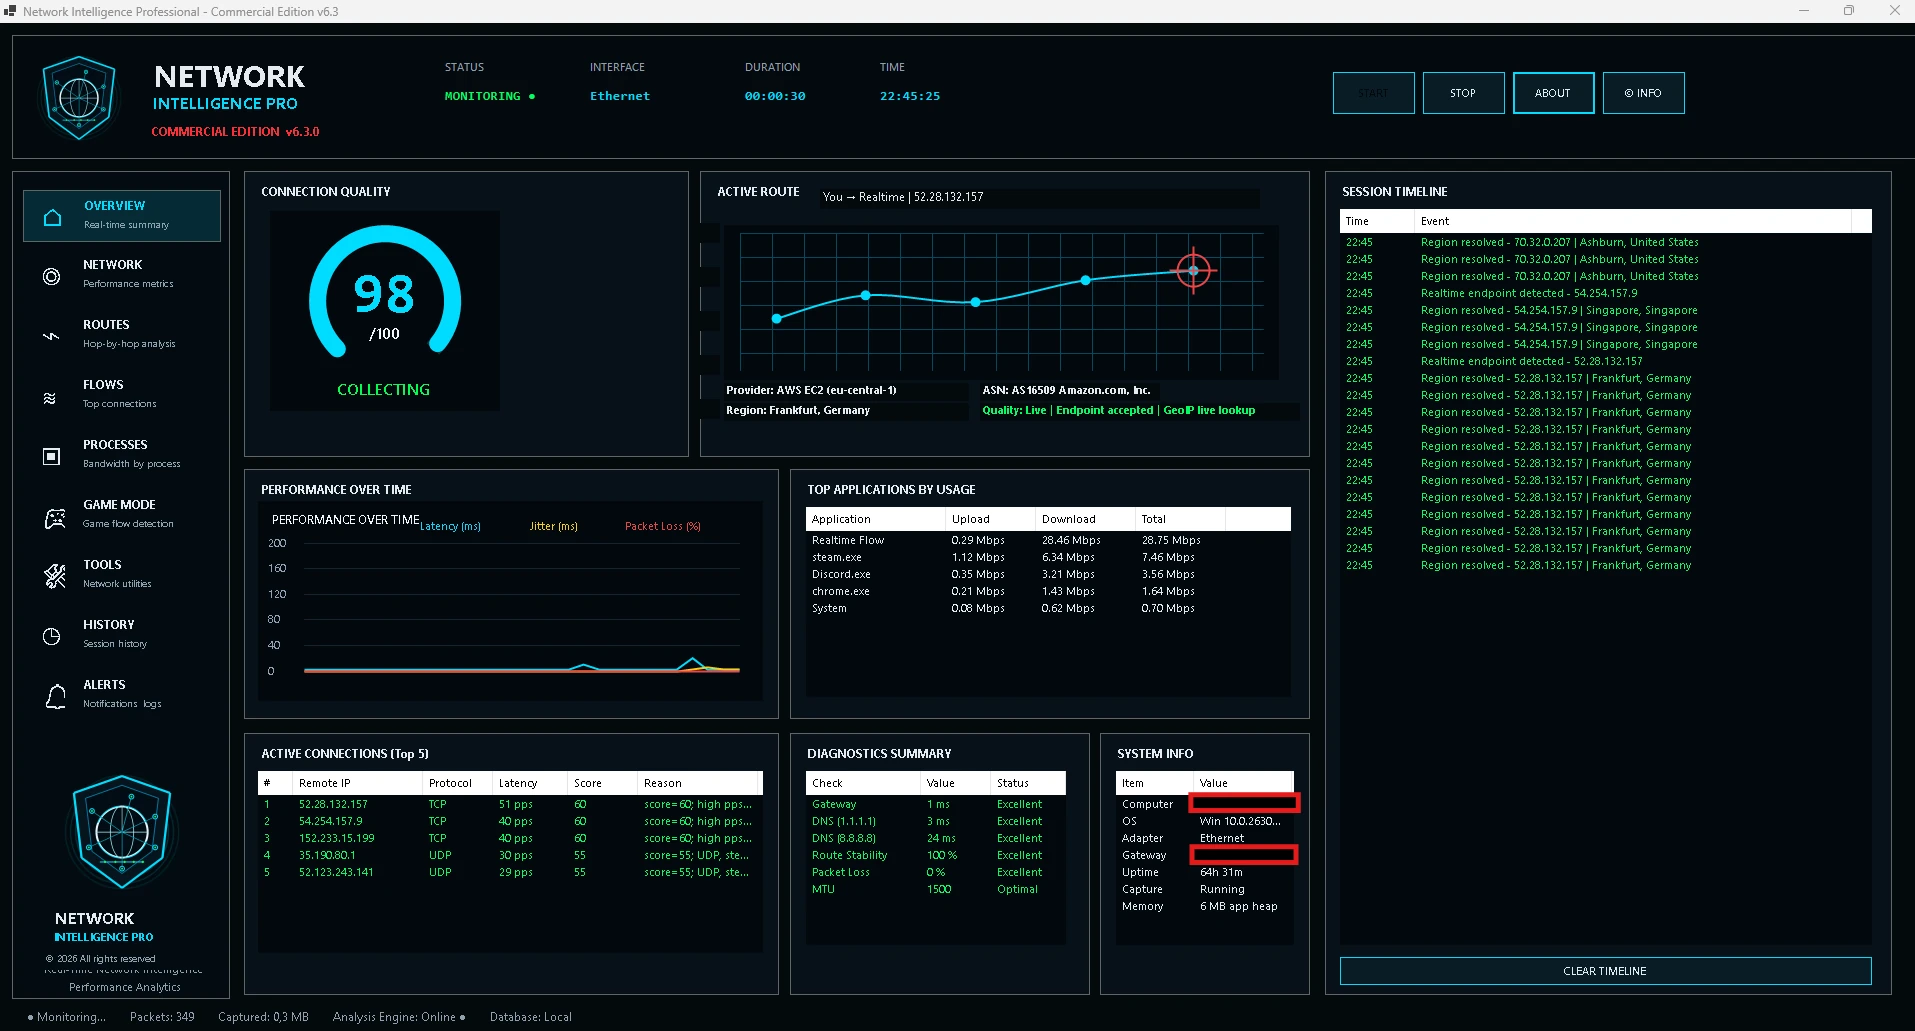
Evidence reviewed: the supplied NetworkIntelligenceProfessional executable and its version resources. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsA Windows interface for defensive website checks, with scan controls, findings and export actions.
Website security findings need a clear review surface that keeps configuration, evidence and recommendations together.
The supplied interface brings target and crawl settings, an explicit scan-authorisation checkbox, a findings table and export actions into one desktop application.
The user supplied an application screenshot showing scan configuration and a completed findings table. Its identity and visible controls can be described; the scanner was not run or independently tested during this review. The earlier standalone .NET launcher still lacks its companion application DLL.
Displayed findings and severity labels are application output, not independently verified vulnerabilities or proof of scan completeness. Target URLs and a cookie value are redacted in the enhanced public preview.
Evidence reviewed: the supplied WebShieldAnalyzer executable and its version resources. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsA controlled path from SOC deployment planning to verified change, with the operator in control.
SOC platform deployment spans multiple services, prerequisites and permissions. Manual steps make it difficult to keep scope, approvals and verification consistent.
A Windows operations dashboard that guides a resumable workflow, starts in dry-run mode, and binds deployment steps to explicit scope and approval evidence.
Implemented Windows toolset with a working pilot history. The inspected source package is v0.26.0. Production approval and activation remain gated; this portfolio makes no production-wide deployment claim. A supplied application screenshot is also included, with the enhanced preview identified separately from the original capture.
The preview is a workflow illustration based on implemented concepts. It is not a screenshot of the Windows application. An original current UI capture is still required before this case study is ready for professional display.
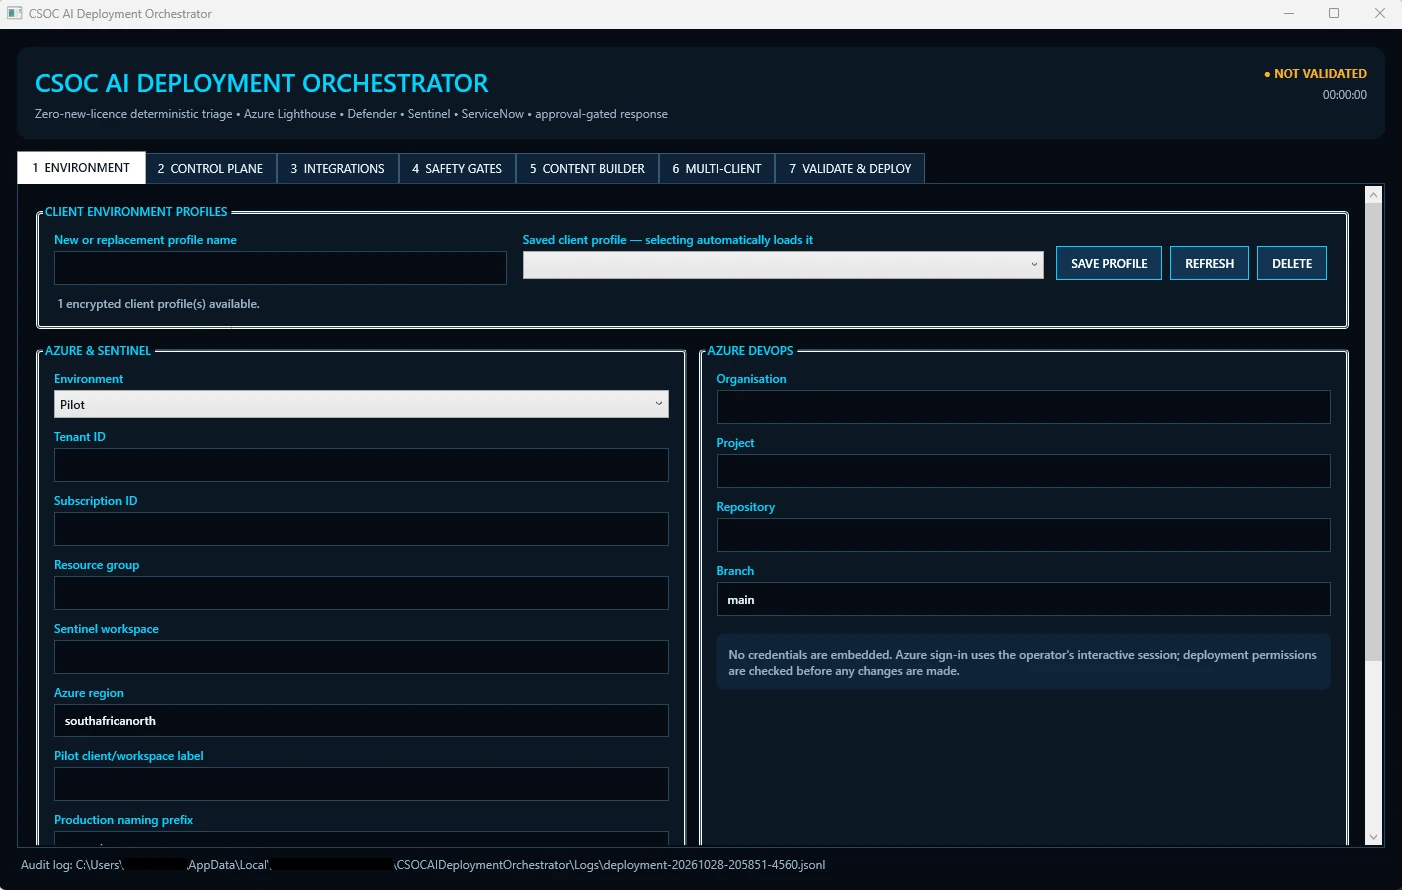
Source review: v0.26.0 package, README and project definition. User-supplied screenshot and separately labelled AI-enhanced preview.
Back to projectsFrom a repeated maintenance call to a clear record of the work, the fee and the payment status.
Property call-outs often arrive as disconnected calls and messages. Repeated visits, agreed fees and payment follow-ups become difficult to track.
An Android app that connects complexes, call-outs, managing agents and billing status in one workflow, with encrypted local records and exportable supporting information.
An Android app with a Google Play release history. The inspected v1.2.0 update is an internal test build and requires device acceptance checks before release. Existing Play availability does not establish that this update is in production.
Payment requests are supporting summaries. This version does not generate formal tax invoices, send email automatically, verify delivery or reconcile payments.
Source review: v1.2.0 internal test kit, managing-agent guide and build definitions.
Back to projectsMake the assumptions behind a telemetry estimate visible, traceable and easy to explain.
A mailbox count alone cannot establish future Sentinel ingestion costs. Estimates need explicit volume assumptions, billing classifications and a verified rate.
A browser-based planning tool that models source-level data volumes, separates free and paid ingestion assumptions, and creates scenarios and client-facing reports.
Completed standalone HTML tool, version 1.0. Its calculations run in the browser and require no tenant connection. This case study describes the delivered implementation; it is not a current Microsoft pricing assessment.
The model produces assumption-based ingestion estimates, not Azure quotes. Rates and billing rules need verification for each assessment. Licences, taxes, extra retention and automation are outside the modeled scope.
Source review: delivered ISR Sentinel Ingestion Estimator HTML application.
Back to projectsPractical cybersecurity. Real understanding.
This is my personal space to share what I’m learning, explain useful ideas and help others build confidence with cybersecurity. You’ll find awareness lessons, technical walkthroughs and lab exercises, written in my own voice.
Personal educational content. Views are my own and do not represent my employer.
Find me on YouTubeSecurity operations, cloud infrastructure and practical engineering.
Cyber Security Engineer · Threat Hunting
Cyber Security Engineer focused on Microsoft Sentinel, Microsoft Defender, and threat hunting. I develop KQL investigations, detection content, and automation for multi-client SOC environments, drawing on extensive cloud and infrastructure experience.
Microsoft certification badges from my CV.
Select a badge to view it.
 SC-100Cybersecurity Architect ExpertView badge
 SC-200Security Operations Analyst AssociateView badge
 SC-900Security, Compliance and Identity FundamentalsView badge
 AZ-104Azure Administrator AssociateView badge
 AZ-140Azure Virtual Desktop SpecialtyView badge
 AZ-800 · AZ-801Windows Server Hybrid Administrator AssociateView badge
 AZ-900Azure FundamentalsView badge
 AI-900Azure AI FundamentalsView badge
Completion is listed in my CV. Current renewal dates are not included.
Formerly Content and Cloud
September 2024 — Present
April 2024 — September 2024
April 2022 — April 2024
December 2016 — April 2022
Earlier technical roles covered infrastructure, Microsoft 365, Intune, identity, endpoint security, and client support.
I.T Network Administrator
Data Capturing
Customer liaison, quotations, tenders, sales, and administration. Desktop support, networking, troubleshooting, and SAP ERP systems.
Administration / Data Capturing
Administration, data capturing, stock control, customer service, and sales.
Public CV version. Direct contact details are omitted.